Our Blog
The October 2026 Hackerstorm Vulnerability Priority Report analyzes 34 critical CISA KEV additions, highlighting aggressive threat actor targeting of network management planes, core operating system kernels, and enterprise edge gateways. Discover essential EPSS scores, sector risk exposures, and strategic remediation priorities to protect your infrastructure.
Reading time 10 minutes
CISA adds 10 actively exploited CVEs to the KEV catalog in October 2026. Learn about critical vulnerabilities and remote code execution risks in Ivanti, GitLab, Cisco, Linux, Broadcom VMware, Adobe, Google, and PHP, plus remediation steps.
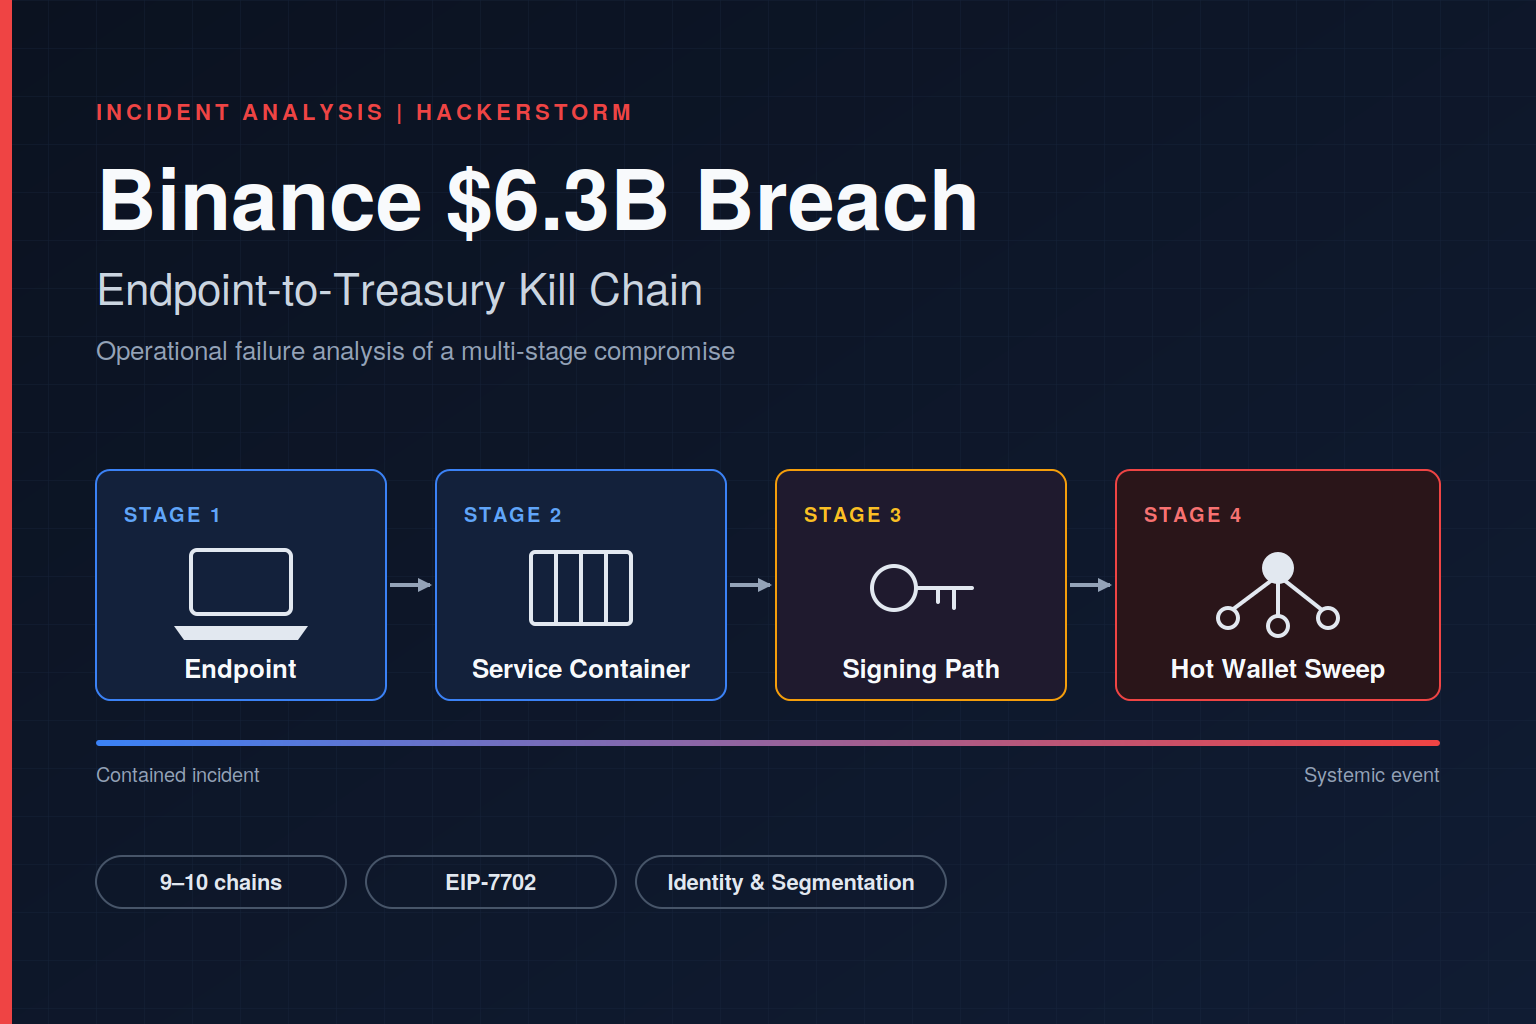
A DevOps laptop may have started the Binance attack that moved about $6.3 billion. What happened, where controls failed, and how to check if the same path exists in your organisation.
Reading time 15 minutes
PHP2Shell reached a CISA KEV listing within six days of the leak, yet public reporting does not show AI was involved. This analysis reviews historical time-to-exploit data, GTIG's AI research and a documented AI-assisted campaign. It separates what the evidence shows about AI and exploitation speed from what remains unproven.
Reading time 15 minutes