Our Blog
The October 2026 Hackerstorm Vulnerability Priority Report analyzes 34 critical CISA KEV additions, highlighting aggressive threat actor targeting of network management planes, core operating system kernels, and enterprise edge gateways. Discover essential EPSS scores, sector risk exposures, and strategic remediation priorities to protect your infrastructure.
Reading time 10 minutes
Security fixes have been released for CVE-2026-109618 and CVE-2026-109619, two PHP memory-handling vulnerabilities tracked as PHP2Shell, each rated 9.2 under CVSS v4.0. Details of the flaws leaked on 20 October, ahead of the scheduled disclosure, and several security vendors reported exploit attempts before the fixes were released, including a honeypot observation four days before public disclosure. Operators should update to a fixed PHP release where available; temporary firewall protections are not a substitute for patching.
Reading time 10 minutes
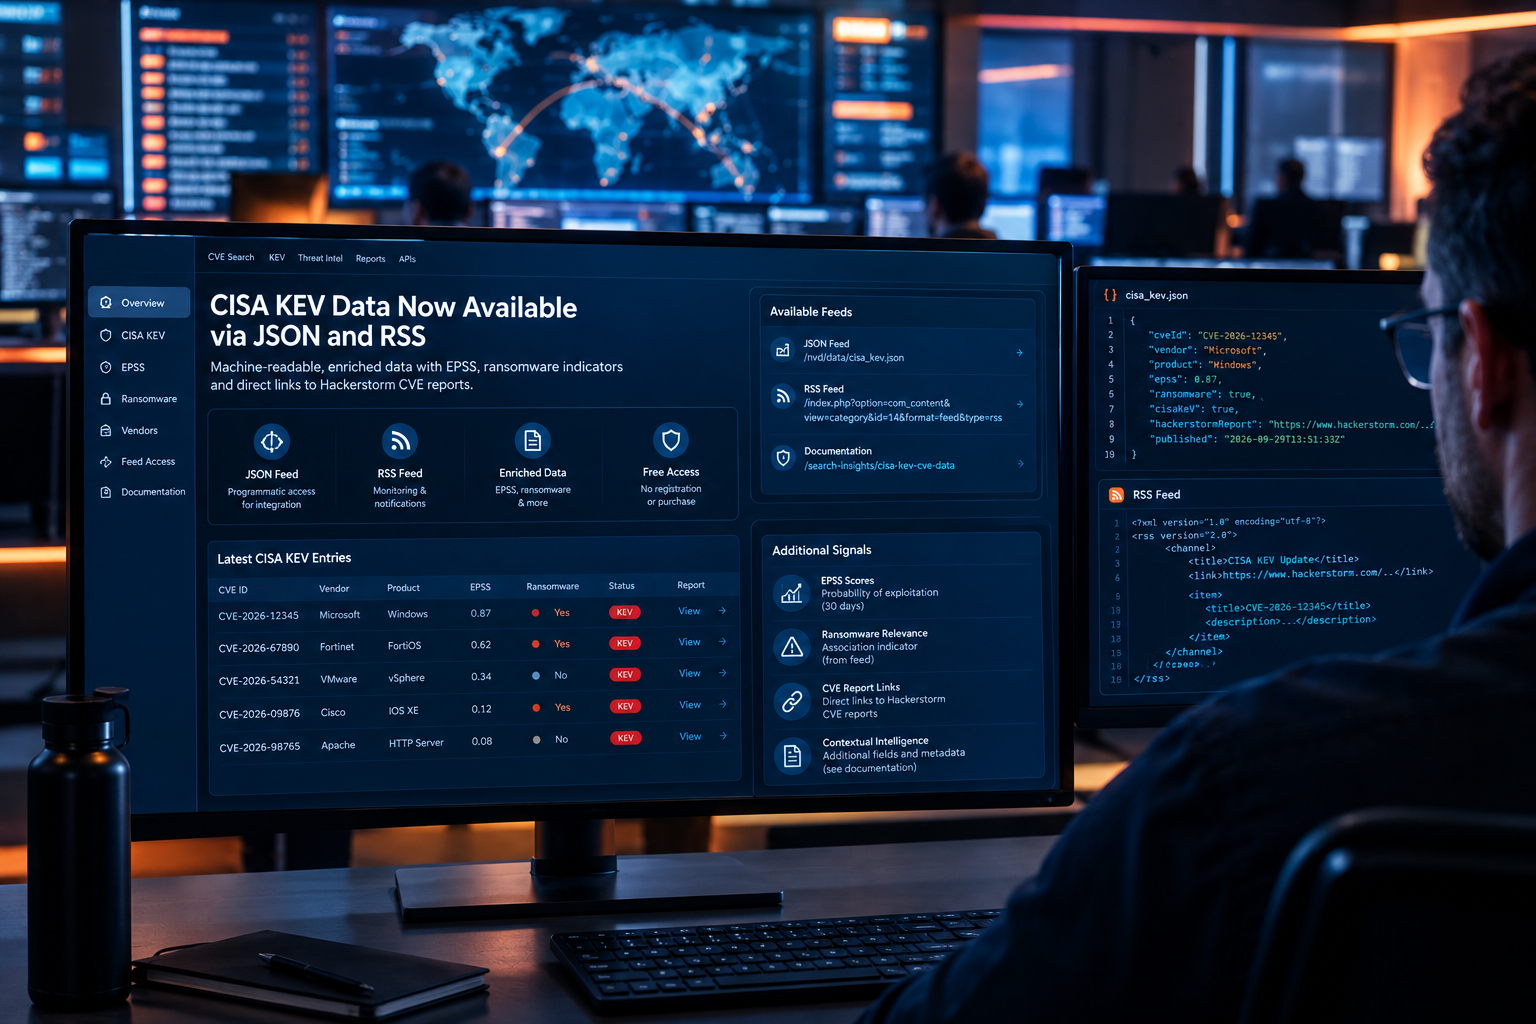
Hackerstorm has made free, machine-readable enriched data based on the latest CISA KEV Catalog available through public JSON and RSS feeds. Designed to help you stay up to date, these feeds enable you to see today’s KEV updates and apply the five signals for risk-based prioritization and remediation.
Reading time 10 minutes
The September 2026 Hackerstorm Vulnerability Priority Report analyzes 43 critical CISA KEV additions, highlighting aggressive threat actor targeting of network management planes, core operating system kernels, and enterprise edge gateways. Discover essential EPSS scores, sector risk exposures, and strategic remediation priorities to protect your infrastructure.
Reading time 10 minutes
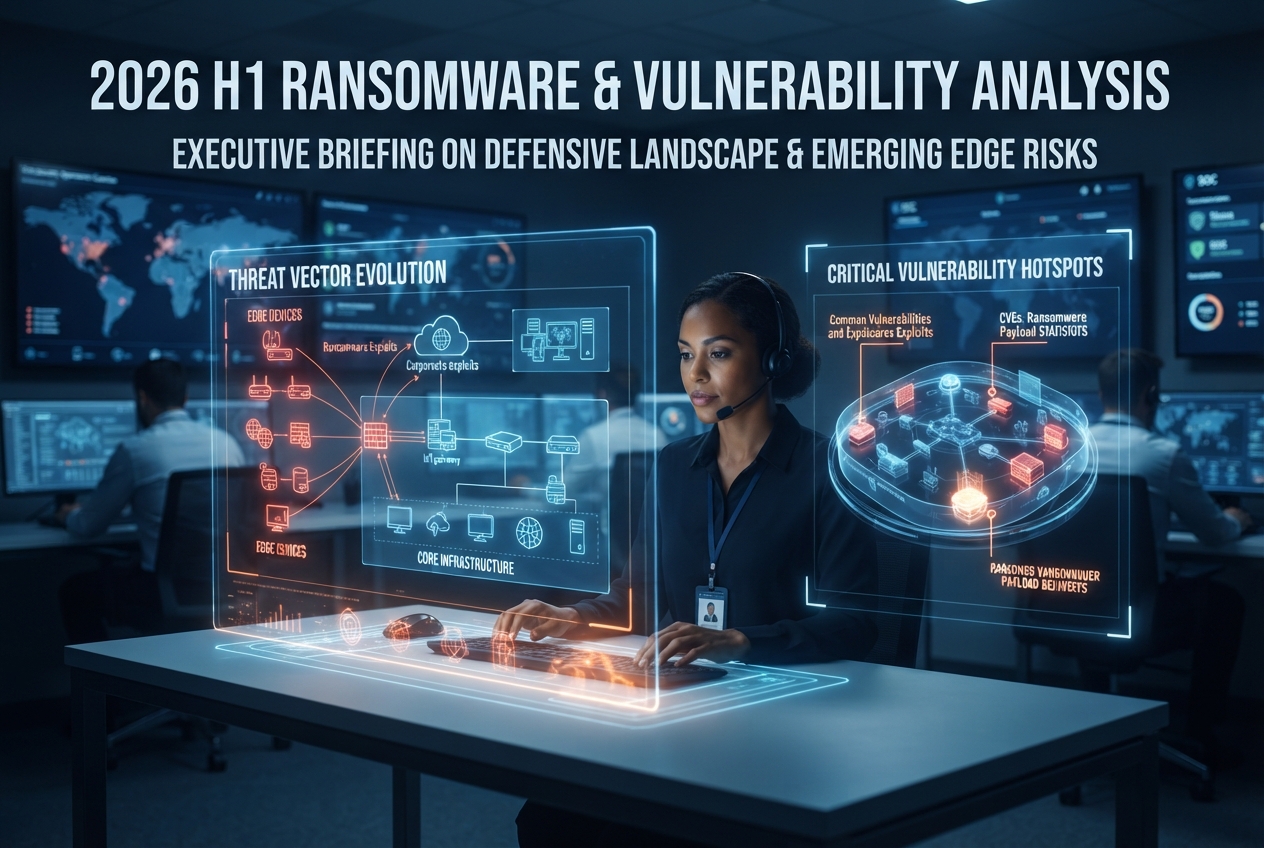
H1 2026 ransomware-linked vulnerabilities reveal a recurring concentration around remote access, network-edge and privileged management infrastructure. Analysis of 20 vulnerabilities shows high levels of exploitation probability, significant business impact and recurring weaknesses involving authentication, deserialization, path traversal and code execution. Six of the 20, nearly a third were actively exploited before a patch or advisory existed at all.
Reading time 10 minutes
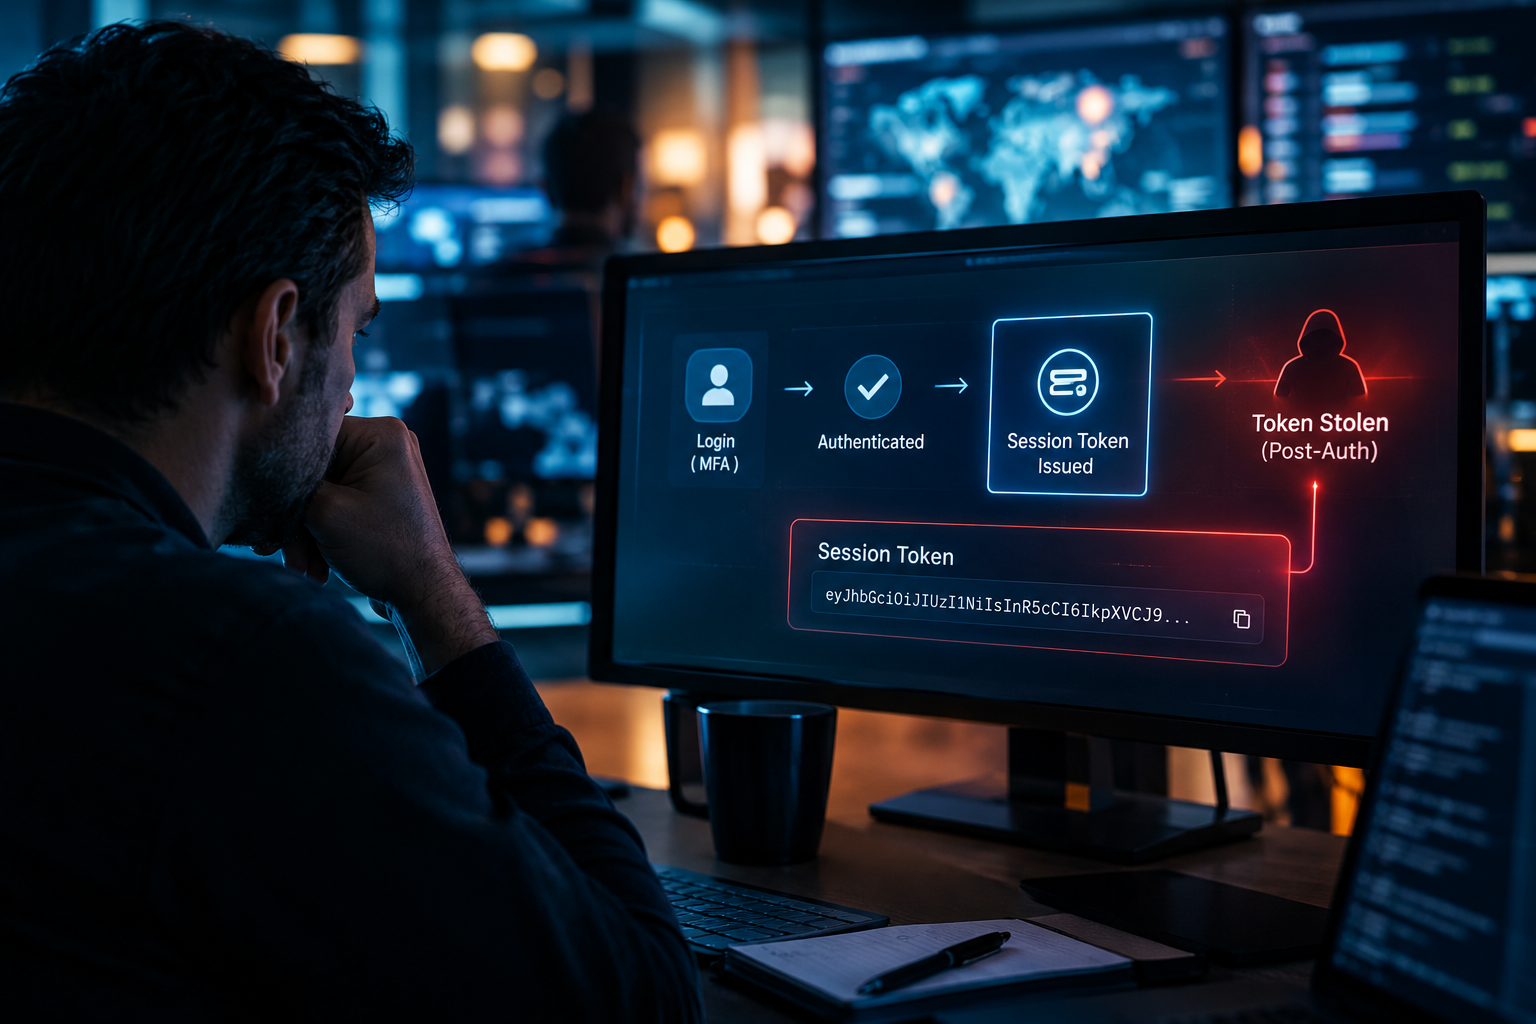
Modern attackers increasingly bypass MFA by stealing session tokens after authentication completes. With median dwell time at 22 seconds for identity-based attacks (Mandiant M-Trends 2025), SOC teams monitoring only authentication gates miss post-authentication compromise entirely. Identity-based initial access represents 65% of breaches (Mandiant) and a material factor in 90% of investigations (Unit 42), yet most organisations treat identity logs as compliance artifacts rather than operational threat intelligence.
Reading time 10 minutes
The CISA Known Exploited Vulnerabilities (KEV) Catalog expanded significantly in August 2026, recording 31 new additions spanning edge appliances, enterprise software, and core operating systems. Active exploitation patterns throughout the month signal a sharp threat actor pivot toward identity infrastructure bypasses, authentication flaws, and remote code execution across ubiquitous enterprise IT dependencies. Security leaders, vulnerability managers, and SOC operations must use this intelligence report to bypass raw severity scores and immediately action operational remediation against confirmed threat activity.
Reading time 10 minutes
Security teams face one new CVE every 7.4 minutes, yet only a fraction of vendor security advisories describe vulnerabilities with meaningful exploitation likelihood or exposure. This analysis maps the evidence separating genuine operational risk from advisory noise, for SOC teams, vulnerability management programmes, and security leadership responsible for prioritisation decisions.
Reading time 10 minutes