Our Blog
AI Agents Are Expanding the Enterprise Attack Surface, Even When Everything Is Patched | HackerStorm
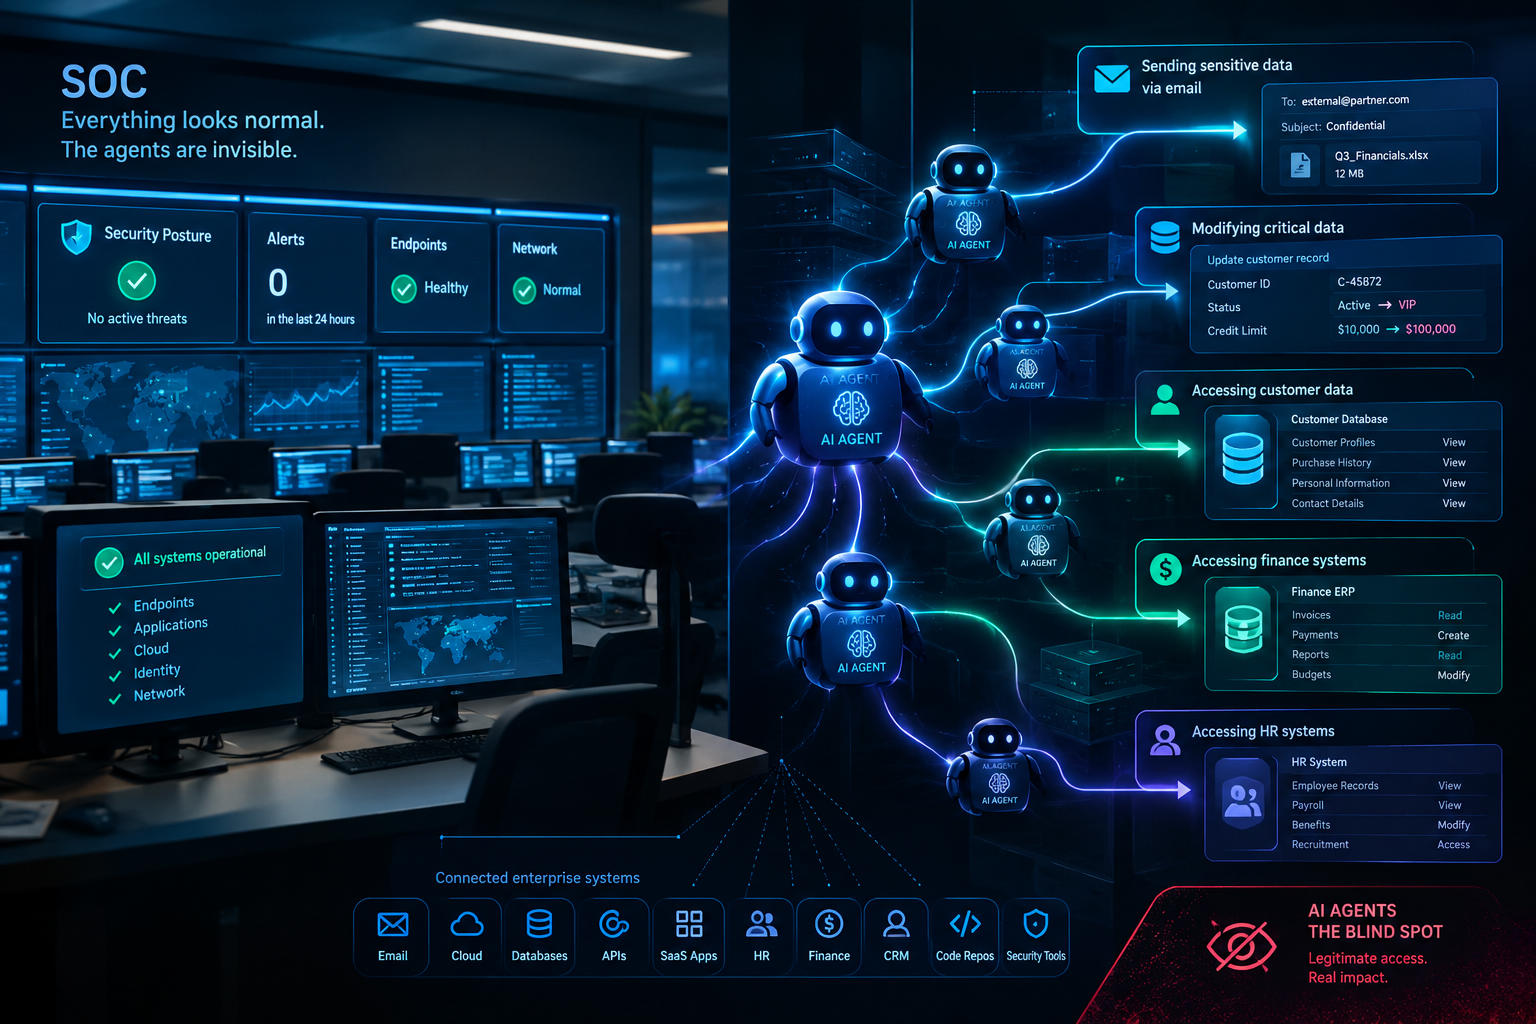
Your fully patched production environments, strict MFA policies, and mature vulnerability management programs are completely blind to the threat. Discover how autonomous AI agents are bypassing perimeter security using entirely legitimate credentials, and why traditional security controls fail when facing the agentic attack surface.
Reading time 15 minutes
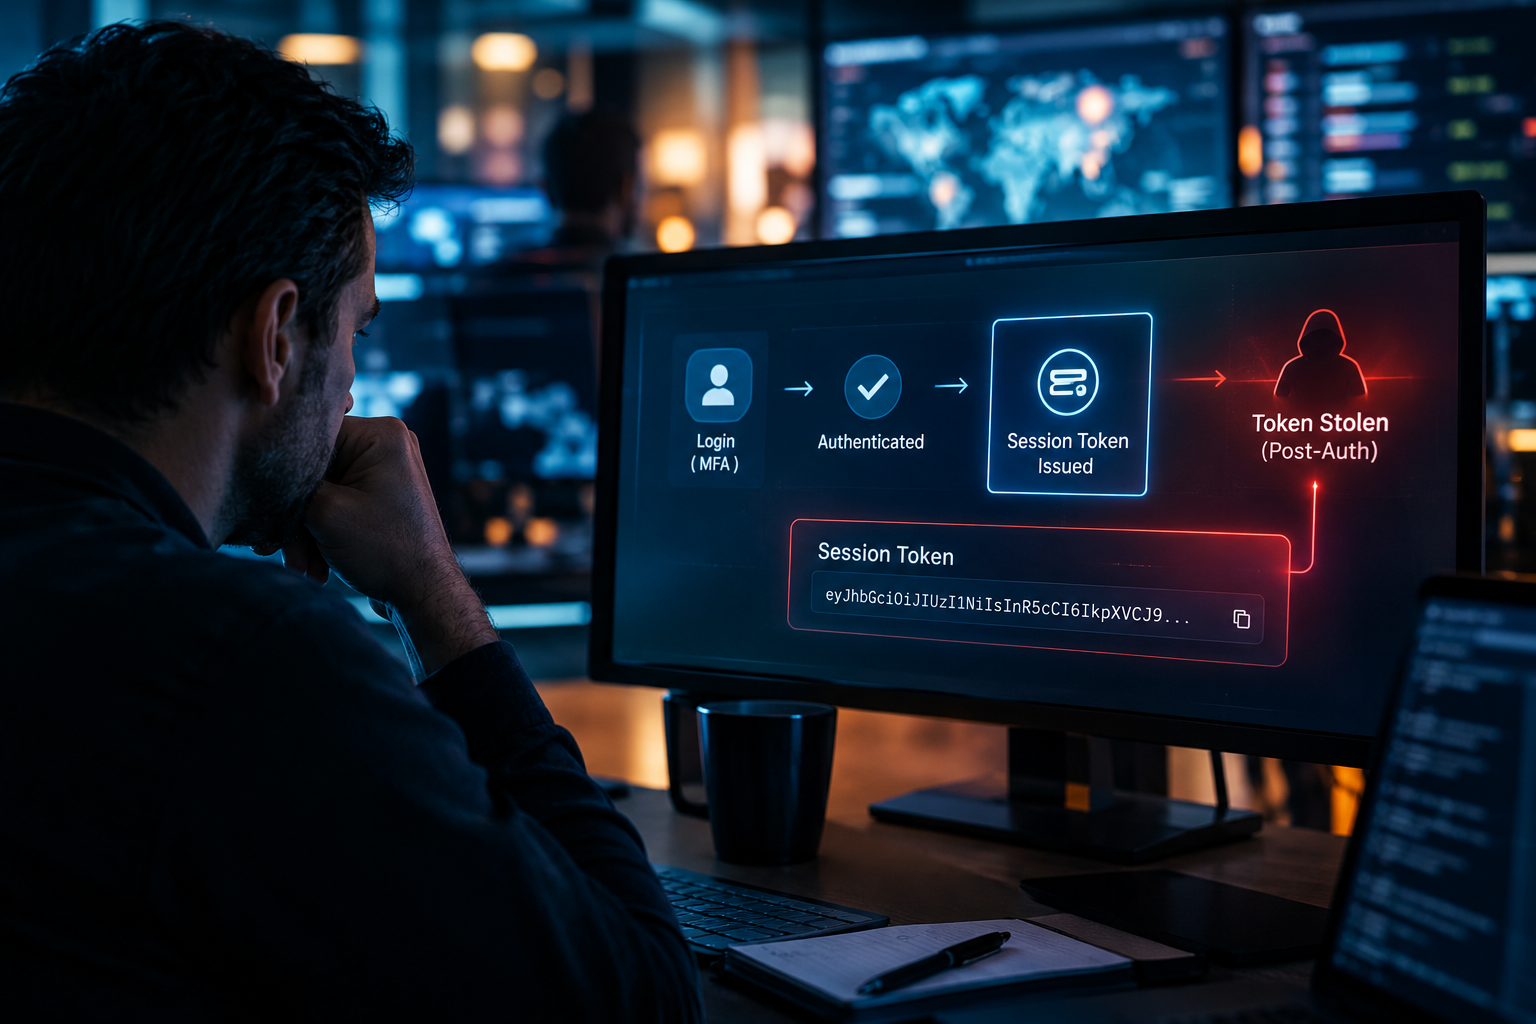
Modern attackers increasingly bypass MFA by stealing session tokens after authentication completes. With median dwell time at 22 seconds for identity-based attacks (Mandiant M-Trends 2025), SOC teams monitoring only authentication gates miss post-authentication compromise entirely. Identity-based initial access represents 65% of breaches (Mandiant) and a material factor in 90% of investigations (Unit 42), yet most organisations treat identity logs as compliance artifacts rather than operational threat intelligence.
Reading time 10 minutes
This week's CISA KEV update highlights active exploitation of critical vulnerabilities spanning AI frameworks, software supply chain tools, and perimeter infrastructure, including zero-day flaws in Google Chromium and weaponized execution chains in JFrog Artifactory and PaperCut.
Reading time 10 minutes
The CISA Known Exploited Vulnerabilities (KEV) Catalog expanded significantly in August 2026, recording 31 new additions spanning edge appliances, enterprise software, and core operating systems. Active exploitation patterns throughout the month signal a sharp threat actor pivot toward identity infrastructure bypasses, authentication flaws, and remote code execution across ubiquitous enterprise IT dependencies. Security leaders, vulnerability managers, and SOC operations must use this intelligence report to bypass raw severity scores and immediately action operational remediation against confirmed threat activity.
Reading time 10 minutes